Legit Security
Legit Security: AI-native ASPM that blocks vulnerable AI-generated code before commit
If your developers live in Cursor, Claude Code or Copilot, Legit answers a question most AppSec stacks still can't: what did the assistant just write, and did it leak something? VibeGuard's inline SAST and SCA before commit are the part that changes outcomes, and the AI inventory gives context on assistants and MCP servers you never formally approved. It's an enterprise ASPM purchase with a demo-led evaluation, not a tool you bolt on in an afternoon.
Verified 1h ago · liveness 74/100 · cite: rightaichoice.com/tools/legit-security
- Enterprises whose developers use Cursor, Claude Code or GitHub Copilot and want vulnerabilities blocked before commit
- AppSec teams drowning in disconnected scanner alerts who need one prioritized, de-duplicated view
- Security leaders who need an inventory of AI models, code assistants and MCP servers in active use
- Organizations enforcing secrets prevention across Git history, ticketing systems and artifact registries
- Small teams hunting for a low-cost standalone static analysis tool
- Organizations with little or no AI coding assistant adoption, where the AI protections go unused
- Teams committed to assembling best-of-breed point scanners instead of a single platform
We scan live Reddit threads, YouTube comments, X posts, G2 reviews and other communities — and hand you an honest verdict in under a minute.
- Honest verdict, not marketing
- Real pros & cons from real users
- Attributed quotes with receipts
3 free scans · no card needed
Skip Legit Security if your developers don't use AI code assistants yet and you only need a single-purpose SAST or SCA scanner, since the VibeGuard IDE blocking and AI Security Command Center inventory are the parts you'd be paying for and not using.
Consolidating results from AST tools you already own still requires connecting and tuning each source, so the unified view takes setup effort before the noise reduction shows up.
Legit Security sits in the enterprise ASPM tier alongside Cycode and Apiiro, aimed at organizations with an AppSec function and meaningful AI coding adoption rather than at solo developers. If budget is your binding constraint, a standalone SAST or SCA tool costs less and skips the platform layer; the consolidation and AI-code governance Legit adds are what you are paying the platform premium for.
In short
Legit Security — Legit Security: AI-native ASPM that blocks vulnerable AI-generated code before commit. Best for Enterprises whose developers use Cursor, Claude Code or GitHub Copilot and want vulnerabilities blocked before commit, AppSec teams drowning in disconnected scanner alerts who need one prioritized, de-duplicated view, Security leaders who need an inventory of AI models, code assistants and MCP servers in active use. Contact Sales pricing.
No head-to-head comparison for Legit Security yet — the alternatives below are the closest matches we list.
What's new in Legit Security
Checked 2 days agoAcross the latest 1 update: 1 launch.
What people actually say about Legit Security — is it worth it?
We ran a structured research pass across product reviews, community discussions, and post-purchase forum threads to surface the patterns vendors won't publish themselves. Below: the recurring strengths, the hidden costs people mention most, and the cohort that consistently regrets adopting this tool.
22 mentions across 3 sources (Hacker News, YouTube, Lemmy) · researched Oct 15, 2026.
Weighted by the 35 posts each of 3 sources contributed.
- +IDE-first scanning that blocks vulnerable AI-generated code before commit, not after the PR
- +Explicit support for Cursor, GitHub Copilot and Windsurf — the assistants teams actually use
- +AI Security Command Center gives real inventory of AI models, MCP servers and shadow AI tooling
- +Policy guardrails and secret-file blocking address the concrete risk of AI sessions leaking credentials
- +AI-native SAST/SCA with reachability and license detection covers OWASP AI Top 10 in one platform
- −No independent user reviews or benchmarks anywhere in the dataset — everything is vendor messaging
- −Cloud-only vendor pricing with no public tiers makes cost planning and comparison difficult
- −Zero value if your developers don't use AI assistants like Cursor or Copilot today
- −Competes head-on with Cycode and Apiiro, both more established in the ASPM category
- −IDE plugin maintenance burden across rapidly changing assistant APIs creates coverage risk
- • No public pricing — expect a procurement cycle, security review and likely a multi-year commitment
- • Implementation and IDE rollout effort across every developer workstation is a real internal cost
- • If you keep your existing SAST/SCA alongside Legit, you're paying twice unless you actually rip one out
- • Plugin maintenance and policy tuning after AI assistant API changes lands on your AppSec team
Viability Score
How well maintained and how widely used is Legit Security? Built from what the vendor actually publishes (docs, changelog, tutorials, integrations, pricing), whether the site is live, and how much real users discuss it. How we calculate this
Last calculated: October 2026
How we score →Key Features
- VibeGuard IDE plugin scans AI-generated code for vulnerabilities before commit
- Real-time SAST and SCA feedback on AI-generated code as developers type
- Blocks unsafe findings inside Cursor, Claude Code and GitHub Copilot
- Feeds remediation insights back into AI coding agents to reduce repeat issues
- AI Security Command Center discovers AI models, code assistants and MCP servers
- Reputation scoring for AI tools with approve, block or flag-for-review actions
- Policy guardrails restrict what files and data AI coding agents can access
- Native SAST and SCA with advanced reachability and license detection
- OWASP AI Top 10 risk coverage
- Consolidates, de-duplicates and prioritizes results from existing AST tools
- Secrets detection across source code, Git history, ticketing systems and artifact registries
- Software supply chain security scanning and policy enforcement
- Agentic remediation agents that propose validated fixes against your workflows
- Application context and business-criticality scoring to prioritize real risk
- Advanced code change management with material change tracking
About Legit Security
Legit Security is an agentic AppSec and Application Security Posture Management platform for AppSec, DevSecOps and product security teams whose developers now write code with AI assistants. The premise is straightforward: legacy scanners see human-authored code, not what Cursor, Claude Code or GitHub Copilot produce, so the platform bolts protection onto the coding session itself and links it to the pipelines, repos and cloud assets underneath. VibeGuard is the entry point. Embedded in the IDE, it runs integrated SAST and SCA in real time on AI-generated code, surfaces secrets and vulnerabilities as developers type, and blocks unsafe findings before commit rather than after the pull request. Findings flow into a centralized console, and remediation insight is fed back into the AI coding agent so fixes train it to introduce fewer issues over time. Around that sits the agentic layer: context and prioritization that weighs business criticality, data sensitivity and exposure; autonomous remediation agents that propose validated fixes against your workflows; native SAST and SCA with reachability and license detection; secrets detection across source, Git history, ticketing and artifact registries; software supply chain and governance controls; and AI Security Command Center discovery of models, code assistants and MCP servers with approve, block or review actions. August 2025 expanded the native scanners with OWASP AI Top 10 coverage and deeper reachability analysis to cut alert noise. The buyer is an enterprise AppSec organization, and the competitive set is Apiiro, Cycode, OX Security and ArmorCode — Legit publishes comparison pages against all four. Its wedge is protecting code at the moment of creation instead of at the pull request.
Behind the Verdict
Where Legit earns its keep is the overlap between AI-assisted development and secrets exposure. A developer prompts an agent, the agent pastes in an internal endpoint with a token, and the credential lands in the diff. VibeGuard catching that before commit is worth more than any dashboard that tells you about it the next morning. The feedback loop is the interesting design choice: remediation insight gets pushed back into the coding agent so the same class of mistake shows up less often. Pick this when you already run a real AppSec program and AI assistants are spreading through your org without a coherent inventory. The AI Security Command Center and policy guardrails give security leaders something concrete to point at, and consolidating noisy AST results into a prioritized view is a genuine time saver for teams drowning in scanner alerts. Pass when adoption is thin. If most of your engineers aren't in an AI IDE, you're paying for a category of protection nobody is exercising, and a leaner SAST or SCA tool will cover the same ground for less. Small teams hunting a cheap standalone linter are also in the wrong aisle. And if your strategy is deliberately best-of-breed point scanners wired together in-house, Legit's consolidation pitch fights your architecture rather than fitting it. The closest comparison is Cycode and Apiiro, with OX Security and ArmorCode also in the frame depending on where your priorities sit. Legit's angle is creation-time protection rather than post-hoc correlation, which matters most when AI-generated code volume is climbing fast. Practical caveat: inline blocking in the IDE is only as good as the adoption behind it. Roll it out broadly and tune the rules, or developers will route around it. The autonomous remediation agents are the piece to
Researching Legit Security? Get your full AI stack in 60 seconds.
Free, no signup — tell us your goal and get tools matched to your budget & existing stack.
Real-world workflow fit
Concrete scenarios for the personas Legit Security actually fits — and what changes day-one when you adopt it.
Roll out VibeGuard into the engineering org's IDEs so AI-generated code is scanned for vulnerabilities, secrets, and policy violations before it ever reaches a commit, with findings streaming into the central console.
Outcome: Secrets and vulnerable patterns get caught at the developer endpoint instead of surfacing later in Git history or a pull request review, and the AppSec team gets one prioritized queue instead of per-editor blind spots.
Turn on the AI Security Command Center to discover every AI model, code assistant, and MCP server in the environment, then review reputation scores and approve, block, or flag each tool.
Outcome: An inventory of sanctioned and unsanctioned AI tooling replaces guesswork, and policy guardrails restrict AI agents from reaching files that commonly hold credentials.
Connect existing AST tools to Legit so it can ingest, de-duplicate, and prioritize findings, while turning on native SAST and SCA with reachability and license detection for the coverage gaps.
Outcome: The team works from a single prioritized list tied to business criticality and code ownership, which cuts triage time and makes remediation targets defensible.
Use Cases
- Block vulnerabilities and secrets in AI-generated code before commit using VibeGuard
- Gain visibility into all AI models, code assistants, and MCP servers in your organization
- Unify findings from SAST, SCA, and secrets scanners into a single prioritized view
- Automate remediation of critical vulnerabilities with AI-powered fix suggestions
- Manage risk in AI-first development programs using vibe coding tools such as Cursor or Windsurf
- Prevent secrets exposure in real-time during pull requests across Git history
- Track material code changes and enforce compliance and governance policies
- Detect shadow development assets and unsanctioned developer accounts
Models Under the Hood
as of 2026-10-16
Limitations
- Legit Security is an enterprise AppSec platform, and its value is concentrated in organizations with real AI coding assistant adoption.
- If your engineers write code by hand, the VibeGuard IDE blocking and AI Security Command Center inventory buy you much less than a narrower SAST or SCA tool would.
- The platform's strength is consolidation — it ingests and de-duplicates results from AST tools you already own — so if you deliberately run best-of-breed point scanners and want to keep tuning each one separately, the unified layer adds a step rather than removing one.
- Deployment covers code to cloud, which means meaningful onboarding work across repositories, CI/CD, and cloud accounts before findings settle down.
as of 2026-10-01
Verification history
We have re-verified Legit Security 22 times since . Each pass re-reads the vendor's own pages and re-checks every listed field against that evidence; passes where nothing had changed are marked as such.
- — re-verified summary, description, our verdict, our analysis, pricing model, pricing tiers, features, integrations, who it suits, who should skip it
- — re-checked, vendor evidence unchanged
- — re-verified summary, description, our verdict, our analysis, pricing model, pricing tiers, features, integrations, who it suits, who should skip it
- — re-verified summary, description, our verdict, our analysis, pricing model, pricing tiers, features, integrations, who it suits, who should skip it
- — re-checked, vendor evidence unchanged
- — re-checked, vendor evidence unchanged
Showing the 6 most recent of 22 verification passes.
Free to cite with attribution — this page re-verifies continuously.
12-month cost
Project the real annual outlay, including the implied monthly cost when only an annual tier is published.
Vendor list price only. Add-on usage, seat overages, and contract minimums are surfaced under Hidden costs & gotchas.
Where the pricing makes sense
The company stage and team size where Legit Security's pricing actually pencils out — and where peers do it cheaper.
Legit Security sits in the enterprise ASPM tier alongside Cycode and Apiiro, aimed at organizations with an AppSec function and meaningful AI coding adoption rather than at solo developers. If budget is your binding constraint, a standalone SAST or SCA tool costs less and skips the platform layer; the consolidation and AI-code governance Legit adds are what you are paying the platform premium for.
Setup time & first value
How long it actually takes to get something useful out of Legit Security — broken out by persona, not the marketing-page minute.
VibeGuard is an IDE plugin and the vendor claims deployment in minutes with immediate results, so a single developer can be protected the same day. The full ASPM rollout — connecting repositories, CI/CD, cloud accounts, and any existing AST scanners for consolidation — is the longer part, typically a staged enterprise onboarding across teams rather than a single-session install.
Switching to or from Legit Security
How to bring data in from common predecessors and how to get it back out — written for the switcher, not the buyer.
- →From a standalone SAST tool: connect it as a source so Legit ingests and de-duplicates its findings, then phase in native SAST where coverage gaps remain
- →From a standalone secrets scanner: move detection to Legit's coverage of source code, Git history, ticketing systems, and artifact registries
- →From a spreadsheet or manual AI-tool inventory: replace it with the AI Security Command Center's discovery and reputation scoring
- →From disconnected point scanners: use Legit's unified view to collapse multiple alert queues into one prioritized list
- ↗To a standalone SAST or SCA tool: if AI code assistant adoption never materializes, a narrower scanner covers the core need at lower cost
- ↗To a competing ASPM platform such as Cycode or Apiiro: expect to re-map policies, scanner connectors, and prioritization rules during the transition
Integrations
Resources & Guides
- Resourcelegitsecurity.com
Legit Security Blog
Insights from Legit Security. Secure your organization
- Resourcelegitsecurity.com
Legit Security Blog
Insights from Legit Security. Secure your organization
- Resourcelegitsecurity.com
ASPM Knowledge Base
This Blog is for ASPM Resources
- Resourcelegitsecurity.com
VibeGuard Resource Hub
VibeGuard Resource Hub
Tutorials & Learning
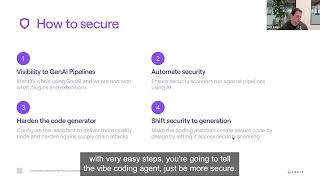
YouTube returned 6 videos for “Legit Security”, and we withheld 5: 5 did not mention Legit Security. Showing the 1 we can prove is about Legit Security.
Official links
Tools that pair well with Legit Security
Common stack mates teams adopt alongside Legit Security, with the specific reason each pairing earns its keep.

Cycode
Agentic development security platform that puts guardrails around AI-written code and remediates findings with agents
Checkmarx
Enterprise AppSec platform that scans AI-generated code across source, dependencies, containers and AI assets, with hybrid Checkmarx Fusion detection and
Wiz
Cloud and AI security platform that connects code, cloud, and runtime into one context graph.
Alternatives to Legit Security
View allCycode
Agentic development security platform that puts guardrails around AI-written code and remediates findings with agents
Frequently Asked Questions
Categories
Best-of guides
Used Legit Security? Help shape our editorial sentiment research.