Orca Security
Agentless cloud-native application protection (CNAPP) platform covering code, cloud, runtime, and AI risk in one view.
Orca Security is a strong pick if you run multi-cloud at scale and want one agentless platform for posture, identity, data, workload, code, and AI risk. The differentiated pieces are SideScanning (no agents to deploy) and the Unified Data Model, which scores findings against live cloud context so developers get a short, genuinely exploitable list instead of thousands of CVEs. It competes most directly with Wiz and Prisma Cloud; if you also need deep endpoint/EDR convergence, CrowdStrike is the closer fit. The trade-off is scope and complexity — CDR, AI agents, and code reachability all need configuration and tuning before you get value.
Verified 8d ago · liveness 78/100 · cite: rightaichoice.com/tools/orca-security
- Enterprises running workloads across two or more clouds
- DevSecOps teams tracing production risk back to code
- Security teams drowning in alerts who need contextual prioritization
- Compliance owners maintaining multi-framework evidence
- Organizations that require agent-based controls for every host by policy
- Teams wanting only basic vulnerability scanning without context
- Buyers seeking an open-source cloud security tool
We scan live Reddit threads, YouTube comments, X posts, G2 reviews and other communities — and hand you an honest verdict in under a minute.
- Honest verdict, not marketing
- Real pros & cons from real users
- Attributed quotes with receipts
3 free scans · no card needed
Skip Orca Security if you need only single-cloud posture checks or basic vulnerability scanning, since you'd be paying for a full CNAPP with CDR, code reachability, and AI security you won't tune or use.
Overlapping tooling you keep paying for: Orca consolidates CSPM, CIEM, DSPM, and CDR, but the savings only land if you actually retire the scanners and dashboards it replaces.
Orca sells on a contact basis, which usually means enterprise-scale contracts; that fits mid-to-large organizations consolidating several cloud security tools. For published rates you'd compare against Wiz, which quotes transparent pricing, or against a narrower point tool if you only need posture checks. Smaller teams often find a focused scanner a better budget fit than a full CNAPP.
In short
Orca Security — Agentless cloud-native application protection (CNAPP) platform covering code, cloud, runtime, and AI risk in one view. Best for Enterprises running workloads across two or more clouds, DevSecOps teams tracing production risk back to code, Security teams drowning in alerts who need contextual prioritization. Contact Sales pricing.
What's new in Orca Security
Checked 8 days agoAcross the latest 1 update: 1 launch.
Viability Score
How well maintained and how widely used is Orca Security? Built from what the vendor actually publishes (docs, changelog, tutorials, integrations, pricing), whether the site is live, and how much real users discuss it. How we calculate this
Last calculated: October 2026
How we score →Key Features
- Agentless SideScanning™ across cloud workloads
- CSPM — cloud security posture management across clouds
- CIEM — cloud identity and entitlement management
- Container and Kubernetes security
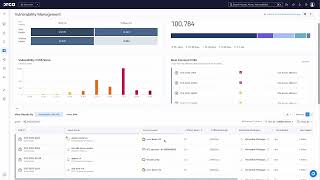
- Agentless vulnerability management with reachability analysis
- DSPM for sensitive data and PII risk
- API discovery, posture management, and drift detection
- Runtime observability and protection via eBPF-based Orca Sensor
- Cloud detection and response (CDR) with 24x7 monitoring
- AI agents for triage, discovery, and remediation
- AI Assistant for natural language querying
- Contextual Security Map for attack path analysis
- Code scanning for IaC, images, secrets, and dependencies
- AI Security — inventory and posture for AI models, packages, and agents
- AI AppGen Security for shadow AI app builders
About Orca Security
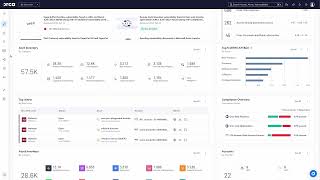
Orca Security is a cloud-native application protection platform (CNAPP) that covers cloud risk across code, cloud, runtime, and AI from a single system. It scans every cloud workload without installing agents using its patented SideScanning technology, and its Unified Data Model correlates misconfigurations, vulnerabilities, identities, sensitive data, and runtime activity so you can see which issues attackers could actually reach. The platform combines CSPM, CWPP, CIEM, DSPM, container and Kubernetes security, API security, multi-cloud compliance, code scanning for IaC/images/secrets/dependencies, and cloud detection and response (CDR) with 24x7 monitoring. Orca AI adds agentic AI for triage, discovery, and remediation plus a natural language assistant, while the Contextual Security Map and dynamic attack-path scoring show how a chain of weaknesses leads to your crown jewels. A newer focus is AI security: inventory every AI model, package, and agent running in your cloud, including shadow AI app builders, then govern posture, data exposure, runtime activity, and compliance from the same platform. An eBPF-based Orca Sensor adds runtime observability and protection where you need it. Orca names representatives for CNAPP in Gartner's 2025 Market Guide and sells primarily to mid-to-large enterprises across finance, media, retail, government, healthcare, and technology. It's a consolidation play: fewer siloed tools, more context per alert, and evidence you can put in front of the board.
Behind the Verdict
Orca's pitch is breadth without agents, and the platform list backs it up: CSPM, CIEM, container and Kubernetes security, vulnerability management, DSPM, API security, multi-cloud compliance, code scanning, CDR, and AI security in one place. The architectural bet is SideScanning — instead of installing sensors on every workload, Orca reads cloud workload snapshots from outside, which is why onboarding is measured in hours rather than weeks and why coverage doesn't depend on your teams finishing a deployment project. The second bet is the Unified Data Model: every misconfiguration, permission, secret, and running process is correlated, so a CVE that no attacker can reach gets down-weighted while a low-severity misconfiguration on a path to sensitive data gets raised. That contextual scoring is what teams actually buy, and it's where the AI agents (triage, discovery, remediation) and the natural-language assistant sit. The current version of the product leans hard into AI, in two directions. One is securing AI: inventory every model, package, and agent in your cloud (including shadow AI app builders), then manage posture, data exposure, runtime activity, and compliance. Orca says a complete AI inventory can be produced in under 30 minutes, and the company extended this coverage to Claude-based AI systems via an integration with Claude's Compliance API. The other direction is using AI inside the product, through agentic workflows and prioritization. Where Orca fits: enterprises running AWS, Azure, GCP, and increasingly Alibaba, Oracle, and Tencent that have outgrown per-cloud native tooling and point scanners, and want a single evidence trail for SOC 2, HIPAA, PCI DSS, and custom frameworks. Where it fits less well: small teams without a dedicated cloud security function, and organizations whose legacy compliance model mandates host-installed agents everywhere — the agentless model is the point, so treating it as a gap is really a requirement mismatch. Because the tool is broad, budget time for tuning CDR, AI agents, and reachability rules before judging alert quality.
Researching Orca Security? Get your full AI stack in 60 seconds.
Free, no signup — tell us your goal and get tools matched to your budget & existing stack.
Real-world workflow fit
Concrete scenarios for the personas Orca Security actually fits — and what changes day-one when you adopt it.
Connect AWS, Azure, and GCP accounts and let SideScanning build a workload inventory without deploying agents, then open the Contextual Security Map to see which misconfigurations and permission paths lead to sensitive data.
Outcome: A prioritized shortlist of genuinely reachable risks and a board-ready view of cloud exposure, produced in the first days rather than after a multi-week agent rollout.
Run code scanning for IaC, images, secrets, and dependencies, then use agentless reachability analysis to check each finding against the live cloud environment before filing tickets in Jira.
Outcome: Developers receive a short list of exploitable issues with the code origin attached, instead of thousands of theoretical CVEs.
Use AI Security to inventory every AI model, package, and agent across the cloud — including shadow AI app builders — and connect Claude-based systems through the Compliance API integration.
Outcome: One governed inventory covering AI posture, data exposure, runtime activity, and compliance evidence.
Use Cases
- Prioritize the vulnerabilities attackers can actually reach by scoring findings against live cloud context.
- Produce a complete inventory of AI models, packages, and agents running in your cloud, including shadow AI.
- Automate continuous compliance evidence for SOC 2, HIPAA, PCI DSS, and custom frameworks across clouds.
- Detect and respond to misconfigurations, runtime threats, and fileless attacks with the Orca Sensor.
- Trace a production risk back to the IaC, image, secret, or dependency that introduced it.
- Replace siloed per-cloud scanners with one agentless platform for posture, identity, and workload risk.
- Give the board a connected view of cloud visibility and the top risks being remediated.
Models Under the Hood
as of 2026-09-15
Limitations
- Orca is a broad platform, so CDR, AI agents, and code reachability analysis need configuration and tuning before they produce useful signal — budget ramp time.
- Compliance coverage and available capabilities can vary by region and by what you have licensed.
- Orca publishes pricing only on a contact basis, so total cost depends on the scope you negotiate rather than a published rate card.
- The agentless model is deliberate, but environments with strict legacy requirements for host-installed agents may need the Orca Sensor deployed alongside their existing tooling.
as of 2026-09-29
Verification history
We have re-verified Orca Security 20 times since . Each pass re-reads the vendor's own pages and re-checks every listed field against that evidence; passes where nothing had changed are marked as such.
- — re-checked, vendor evidence unchanged
- — re-checked, vendor evidence unchanged
- — re-checked, vendor evidence unchanged
- — re-checked, vendor evidence unchanged
- — re-checked, vendor evidence unchanged
- — re-verified summary, description, our verdict, our analysis, pricing model, pricing tiers, features, integrations, who it suits, who should skip it
Showing the 6 most recent of 20 verification passes.
Free to cite with attribution — this page re-verifies continuously.
Where the pricing makes sense
The company stage and team size where Orca Security's pricing actually pencils out — and where peers do it cheaper.
Orca sells on a contact basis, which usually means enterprise-scale contracts; that fits mid-to-large organizations consolidating several cloud security tools. For published rates you'd compare against Wiz, which quotes transparent pricing, or against a narrower point tool if you only need posture checks. Smaller teams often find a focused scanner a better budget fit than a full CNAPP.
Setup time & first value
How long it actually takes to get something useful out of Orca Security — broken out by persona, not the marketing-page minute.
For a multi-cloud enterprise already using cloud-native security tooling: hours to first visibility, since SideScanning needs no agent rollout — expect the first prioritized risk view the same day. Allow a few weeks of tuning before CDR, AI agents, and code reachability are calibrated to your environment. For a single-cloud team, onboarding is quick but the platform's value takes longer to
Switching to or from Orca Security
How to bring data in from common predecessors and how to get it back out — written for the switcher, not the buyer.
- →From per-cloud native tools (AWS Security Hub, Azure Defender for Cloud, GCP Security Command Center): connect the same accounts to Orca and consolidate posture, identity, and workload findings into one view.
- →From point scanners (vulnerability, DSPM, or API security tools): map their findings to Orca's Unified Data Model and retire each tool as coverage is verified.
- →From an agent-based CNAPP: deploy SideScanning agentlessly first, then use the Orca Sensor only where runtime protection is genuinely required.
- ↗To Wiz: if published, transparent pricing matters more to you than agentless snapshot scanning.
- ↗To CrowdStrike: if you want cloud risk converged with endpoint detection and response in one console.
- ↗To a single-cloud native suite: if your estate is confined to one hyperscaler and a full CNAPP is more scope than you need.
Integrations
Resources & Guides
- Resourceorca.security
Blog
The Orca Cloud Security Platform delivers the world's most comprehensive coverage and visibility of risks across the cloud. Read our most recent blog posts!
- Resourceorca.security
Resource Library
Check out Orca's Resource Library for everything you need to know about agentless cloud infrastructure security and compliance for AWS, Azure, and GCP.
Tutorials & Learning
Official links
Tools that pair well with Orca Security
Common stack mates teams adopt alongside Orca Security, with the specific reason each pairing earns its keep.
Field Effect
Field Effect MDR: AI-native managed detection and response covering endpoint, cloud and network, with native AI governance for shadow AI
Checkmarx
Checkmarx One is an AI-native application security platform that unifies SAST, SCA, DAST, container and AI-supply-chain scanning under one correlated risk view.
SentinelOne Singularity
SentinelOne Singularity is an AI-native endpoint, identity, and cloud security platform that autonomously detects and responds to threats
Featured Head-to-Head Comparisons
Alternatives to Orca Security
View all
Field Effect
Field Effect MDR: AI-native managed detection and response covering endpoint, cloud and network, with native AI governance for shadow AI
Checkmarx
Checkmarx One is an AI-native application security platform that unifies SAST, SCA, DAST, container and AI-supply-chain scanning under one correlated risk view.
SentinelOne Singularity
SentinelOne Singularity is an AI-native endpoint, identity, and cloud security platform that autonomously detects and responds to threats
Frequently Asked Questions
Best-of guides
Topics
Used Orca Security? Help shape our editorial sentiment research.