Agent Vault
Open-source credential broker that stops AI agents from leaking real API keys via prompt injection
If your agents run with real API keys in their environment, Agent Vault removes the single most exploitable path in that setup. It's narrower than HashiCorp Vault or Doppler by design, and it asks you to run and babysit a proxy. For teams using Claude Code or OpenClaw in anything resembling production, that tradeoff is usually worth it.
Verified 2d ago · liveness 75/100 · cite: rightaichoice.com/tools/agent-vault
- Security engineers running remote coding agents with real API keys in the environment
- Platform teams building custom agent harnesses that need credential brokering
- Operators offering ephemeral sandboxed agents to untrusted users
- Organizations enforcing credential security across AI agent workflows
- Non-technical users without the ability to self-host and maintain a proxy
- Teams that want a fully managed SaaS credential vault and no infrastructure
- Workflows where the agent must legitimately read or handle the real secret itself
We scan live Reddit threads, YouTube comments, X posts, G2 reviews and other communities — and hand you an honest verdict in under a minute.
- Honest verdict, not marketing
- Real pros & cons from real users
- Attributed quotes with receipts
3 free scans · no card needed
Skip Agent Vault if you are a non-technical user, need a fully managed SaaS vault without self-hosting, or your agents must handle real secrets directly—otherwise the operational overhead isn't worth it.
Self-hosting requires server resources and ongoing maintenance, which is a time and infrastructure cost.
The open-source tier is free but requires self-hosting. For teams needing support and SLAs, the enterprise managed edition via Infisical incurs cost—compare with HashiCorp Vault's paid tiers, which are more expensive but don't prevent exfiltration.
In short
Agent Vault — Open-source credential broker that stops AI agents from leaking real API keys via prompt injection. Best for Security engineers running remote coding agents with real API keys in the environment, Platform teams building custom agent harnesses that need credential brokering, Operators offering ephemeral sandboxed agents to untrusted users. Free to use.
What people actually say about Agent Vault — is it worth it?
We ran a structured research pass across product reviews, community discussions, and post-purchase forum threads to surface the patterns vendors won't publish themselves. Below: the recurring strengths, the hidden costs people mention most, and the cohort that consistently regrets adopting this tool.
44 mentions across 4 sources (Hacker News, Product Hunt, GitHub, Lemmy) · researched Jul 30, 2026.
Average across the 4 sources that answered — each source counts once, not each post.
- +Prevents credential exfiltration via prompt injection effectively.
- +Open-source and self-hosted with no vendor lock-in.
- +Supports integration with HashiCorp Vault and Bitwarden.
- +Active development with responsive maintainers on GitHub.
- +Works with popular agents like Claude Code and Codex.
- −MITM setup requires trust in the proxy itself.
- −Only supports HTTP/HTTPS, not other protocols.
- −Setup can be complex for non-developer users.
- −Some features like websocket auth are not yet supported.
- −Competing tools like Claw Patrol offer broader protocol support.
- • Self-hosting requires infrastructure (server, networking)
- • Enterprise pricing not publicly disclosed
Viability Score
How well maintained and how widely used is Agent Vault? Built from what the vendor actually publishes (docs, changelog, tutorials, integrations, pricing), whether the site is live, and how much real users discuss it. How we calculate this
Last calculated: September 2026
How we score →Key Features
- Credential broker that substitutes dummy credentials like __anthropic_api_key__ with real secrets
- MITM proxy intercepts outbound HTTP and HTTPS traffic from agents
- Self-hosted deployment via binary or Docker on a separate host
- Management UI and API on port 14321
- MITM proxy listening on port 14322
- Bootstrap agent environment with AGENT_VAULT_ADDR, AGENT_VAULT_TOKEN, AGENT_VAULT_VAULT
- Multiple credential stores including Infisical and plaintext
- Service rules match target host and inject the correct credential
- Short-lived token minting for ephemeral sandboxed agents
- Route any HTTP-capable agent via API, CLI, SDK, or MCP
- Dedicated setup guides for Claude Code, Cursor, Codex, OpenClaw, Hermes Agent, and OpenCode
- Replaces auth headers entirely when constructing upstream requests
- Works with LLM providers, GitHub, Stripe, and other HTTP services
About Agent Vault
Agent Vault is an open-source credential broker and MITM proxy from Infisical that sits between AI agents and the APIs they call. It covers LLM providers, GitHub, Stripe, and other HTTP services. Agents like Claude Code, Cursor, Codex, and OpenClaw route their outbound requests through a Vault server, which swaps dummy credentials such as __anthropic_api_key__ or __github_pat__ for the real ones (or replaces auth headers entirely) before forwarding upstream. The real secret never enters the agent's process, so a prompt-injection payload has nothing to steal. The motivation is straightforward: traditional secret management returns credentials to your applications, which is the wrong model for agents that can be manipulated by untrusted input. HashiCorp Vault and Doppler store and distribute secrets well, but they don't stop an agent from exfiltrating what it holds. Agent Vault is built for security engineers and platform teams running remote coding agents, all-purpose agents, custom harnesses, and ephemeral sandboxes. Deployment is self-hosted on a separate host: install the binary or run Docker, then configure credentials, service rules, and an agent representation to get a token. A management UI on port 14321 and a MITM proxy on port 14322 handle administration and traffic interception. You bootstrap the agent environment with the Agent Vault CLI and AGENT_VAULT_ADDR, AGENT_VAULT_TOKEN, and AGENT_VAULT_VAULT. Credential stores include Infisical and plaintext, and service rules match target hosts to inject the right credential. It works with any HTTP-capable agent via API, CLI, SDK, or MCP. For orchestrators spinning up sandboxes, a short-lived token can be minted per sandbox. Compared with general-purpose vaults, Agent Vault trades operational overhead for a control traditional tools don't provide: agents authenticate without holding secrets. An enterprise managed edition via Infisical adds support, SLAs, and advanced features for teams that don't want to run
Behind the Verdict
Most secret managers solve distribution: get the key to the workload. Agent Vault solves a different problem, which is that the workload is now an LLM that can be talked into leaking. We'd reach for it the moment an agent holds credentials it doesn't strictly need to see. The dummy-substitution model is the part that matters. Your agent sees __github_pat__, the proxy swaps in the real token on the way out, and prompt injection has no target. That's a cleaner guarantee than trying to filter malicious prompts, which is a losing game. The mechanics are sensible. A management UI on 14321, a MITM proxy on 14322, service rules keyed on target host, credential stores including Infisical and plaintext, and an agent construct that supports minting short-lived tokens for sandboxes. Setup runs through the CLI with AGENT_VAULT_ADDR, AGENT_VAULT_TOKEN, and AGENT_VAULT_VAULT. It works with any HTTP-capable agent over API, CLI, SDK, or MCP, and there are dedicated guides for Claude Code, Cursor, Codex, OpenClaw, Hermes Agent, and OpenCode. Where it bites is operations. You're standing up and maintaining a proxy on a separate host, defining service rules, and keeping operator access private or behind TLS and auth. That's real work, and it doesn't shrink because the tool is open source. If you want a managed path, the Infisical enterprise edition is the answer, but it comes with a sales conversation and likely a contract. The closest alternative is just using Infisical or HashiCorp Vault the way you already do. Those handle storage and rotation fine. They don't prevent an agent from leaking a credential it was handed, which is the specific failure Agent Vault was built to close. Teams with minimal security requirements or no self-hosting appetite should pass; the overhead isn't
Researching Agent Vault? Get your full AI stack in 60 seconds.
Free, no signup — tell us your goal and get tools matched to your budget & existing stack.
Real-world workflow fit
Concrete scenarios for the personas Agent Vault actually fits — and what changes day-one when you adopt it.
You want to let developers use Claude Code with real API keys without risking key leakage via prompt injection.
Outcome: You self-host Agent Vault, configure dummy credentials, and bootstrap Claude Code with AGENT_VAULT_ADDR and token. All API calls are proxied securely, and keys never enter the agent's process.
You offer ephemeral coding agents to external users and need to control API access securely.
Outcome: An orchestrator mints short-lived tokens for each sandbox, agents use dummy credentials, and Agent Vault injects real ones on the fly, preventing leaks.
Use Cases
- Secure Claude Code sessions by routing all API calls through Agent Vault to prevent API key theft.
- Deploy ephemeral coding agents in sandboxes where agents use dummy credentials that the vault substitutes in transit.
- Integrate with OpenClaw or Hermes Agent to proxy GitHub/Stripe calls without exposing secrets.
- Run a multi-tenant agent platform where each agent gets a short-lived token linked to vault credentials.
- Adopt as a security layer in CI/CD pipelines to protect API keys used by agentic scripts.
Limitations
- Open-source self-hosted credential broker that requires running and maintaining your own Agent Vault server and MITM proxy.
- Remote administration is not built in: the operator must configure TLS and authentication (SSO reverse proxy, IP allowlist, or VPN) to expose the management UI/API on port 14321 safely.
- There is no managed free tier; Infisical offers a separate managed enterprise option with support and SLAs.
as of 2026-08-29
Verification history
We have re-verified Agent Vault 5 times since . Each pass re-reads the vendor's own pages and re-checks every listed field against that evidence; passes where nothing had changed are marked as such.
- — re-verified summary, description, our verdict, our analysis, pricing model, pricing tiers, features, integrations, who it suits, who should skip it
- — re-verified summary, description, our verdict, our analysis, pricing model, pricing tiers, features, integrations, who it suits, who should skip it
- — re-verified summary, description, our verdict, our analysis, pricing model, pricing tiers, features, integrations, who it suits, who should skip it
- — re-checked, vendor evidence unchanged
- — re-verified summary, description, our verdict, our analysis, pricing model, pricing tiers, features, integrations, who it suits, who should skip it
Free to cite with attribution — this page re-verifies continuously.
12-month cost
Project the real annual outlay, including the implied monthly cost when only an annual tier is published.
Vendor list price only. Add-on usage, seat overages, and contract minimums are surfaced under Hidden costs & gotchas.
Plans compared
For each published Agent Vault tier: who it actually fits, and what it adds vs. the previous tier. Cross-reference the cost calculator above for projected annual outlay.
Open Source
$0
Ideal for
Security-conscious developers and small teams willing to self-host and manage the proxy for direct control over agent credential security.
What this tier adds
Starting tier: free, self-hosted credential broker with management UI, CLI, and support for Infisical/plaintext stores.
Enterprise (managed via Infisical)
Custom
Where the pricing makes sense
The company stage and team size where Agent Vault's pricing actually pencils out — and where peers do it cheaper.
The open-source tier is free but requires self-hosting. For teams needing support and SLAs, the enterprise managed edition via Infisical incurs cost—compare with HashiCorp Vault's paid tiers, which are more expensive but don't prevent exfiltration.
Setup time & first value
How long it actually takes to get something useful out of Agent Vault — broken out by persona, not the marketing-page minute.
For a single coding agent like Claude Code, expect 15-30 minutes: install the binary or Docker, configure credentials and rules, and bootstrap the agent. For multi-tenant sandboxes, add time for orchestrator setup and token minting.
Switching to or from Agent Vault
How to bring data in from common predecessors and how to get it back out — written for the switcher, not the buyer.
- →From HashiCorp Vault: Move credentials to Infisical or plaintext store, then define service rules in Agent Vault to replace direct secret access.
- ↗To Infisical: If you need a managed vault without proxy features, adopt Infisical's native secret management.
Integrations
Resources & Guides
Tutorials & Learning
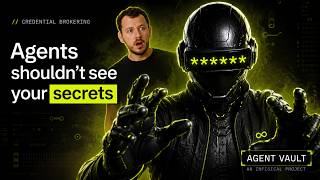
YouTube returned 6 videos for “Agent Vault”, and we withheld 5: 5 did not mention Agent Vault. Showing the 1 we can prove is about Agent Vault.
Official links
Featured Head-to-Head Comparisons
Agent Vault vs Temporal Ai
If you need your AI agents to survive crashes and recover state automatically, choose Temporal AI. If your primary concern is preventing credential exfiltration from AI agents via prompt injection, go with Agent Vault. Both are open-source freemium tools — Temporal focuses on reliability and orchestration; Agent Vault focuses on security and secret isolation.
Agent Vault vs Push Security
Choose Push Security if you need a comprehensive browser security platform to defend against AI-powered phishing, session hijacking, and shadow AI usage across all browsers. Choose Agent Vault if you are a developer who needs an open-source way to prevent credential exfiltration from AI coding agents. They solve different problems—Push secures the human browsing experience, Agent Vault secures machine-to-machine agent calls.
Agent Vault vs Audioeye
Agent Vault vs Mostly Ai
Mostly AI and Agent Vault solve completely different problems. Pick Mostly AI if your priority is generating high-fidelity synthetic data for ML training or analytics under privacy constraints. Pick Agent Vault if you run AI coding agents and need a simple, self-hosted way to stop credential leaks from prompt injection. They complement each other rather than compete.
Popular in AI Governance & Guardrails
Mindgard
Automated AI red teaming platform that continuously discovers, assesses, and defends AI systems and agents.
Poolside AI
Open-weight agentic coding models — Laguna XS 2.1 and Laguna S 2.1 — built for secure on-prem and air-gapped enterprise AI.
Olas Network
Co-own, deploy, and monetize AI agents on-chain with Olas.
Frequently Asked Questions
Best-of guides
Used Agent Vault? Help shape our editorial sentiment research.