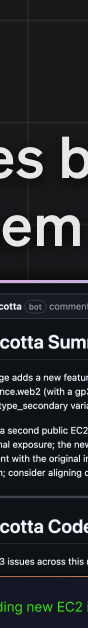
Terracotta AI
Terracotta AI reviews every Terraform pull request for security, compliance, cost, and drift — inside the PR, before you merge.
If your infrastructure lives in Terraform and you have more than one person merging to it, Terracotta AI is worth a serious look. The review comment is the product: SSH open to 0.0.0.0/0, an unencrypted S3 bucket, a +$243/mo instance bump, and a resource someone edited in the console — all surfaced on the PR with an 'Open fix PR' remediation path. The drift view (119 AWS resource types) and the blast-radius view are the two features that are hardest to reproduce with a linter. It is not a general code reviewer, and it is Terraform/OpenTofu-centric, so check your stack before you commit. For teams that want one tool covering many languages, pair it with or compare against Checkov and Snyk;
Verified 11d ago · liveness 72/100 · cite: rightaichoice.com/tools/terracotta-ai
- Platform teams enforcing IaC standards across many repos
- SRE and DevOps teams reviewing high volumes of Terraform PRs
- Security engineers needing pre-deployment findings with an audit trail
- Regulated organizations (healthcare, finance) collecting SOC 2 / HIPAA evidence
- Teams whose infrastructure as code is not Terraform-family
- Teams using a Git provider other than GitHub or GitLab
- Application-code review (Terracotta reviews infrastructure code)
We scan live Reddit threads, YouTube comments, X posts, G2 reviews and other communities — and hand you an honest verdict in under a minute.
- Honest verdict, not marketing
- Real pros & cons from real users
- Attributed quotes with receipts
3 free scans · no card needed
Skip Terracotta AI if your infrastructure code is not Terraform or OpenTofu, or if your repositories live somewhere other than GitHub or GitLab — the review only runs where it is connected.
Cost impact is reported as an estimated monthly and annual projection from resource configuration, so treat it as a directional figure to investigate rather than a line on your cloud bill.
The vendor publishes a free entry point for individuals, a Team tier at $49/seat/mo, and an Enterprise tier at contact sales with SSO/SAML, self-hosted deployment, custom audit log export, and air-gapped support. That puts Terracotta in the same band as other seat-priced developer security tooling: cheaper than an enterprise code-scanning contract, more than a standalone open-source scanner you run yourself. Per-seat pricing means the bill tracks how many engineers merge infrastructure, not how
In short
Terracotta AI — Terracotta AI reviews every Terraform pull request for security, compliance, cost, and drift — inside the PR, before you merge. Best for Platform teams enforcing IaC standards across many repos, SRE and DevOps teams reviewing high volumes of Terraform PRs, Security engineers needing pre-deployment findings with an audit trail. Free to start; paid plans from $49/user/mo.
What people actually say about Terracotta AI — is it worth it?
We ran a structured research pass across product reviews, community discussions, and post-purchase forum threads to surface the patterns vendors won't publish themselves. Below: the recurring strengths, the hidden costs people mention most, and the cohort that consistently regrets adopting this tool.
14 mentions across 2 sources (Hacker News, Lemmy) · researched Jul 3, 2026.
Average across the 2 sources that answered — each source counts once, not each post.
- +Specialized in IaC — understands Terraform, Pulumi, CloudFormation semantics.
- +Natural language policy creation avoids complex scripting.
- +Y Combinator backed — some pedigree in startup execution.
- +Freemium model lowers barrier for individual developers.
- +CIS and SOC2 compliance rules out of the box.
- −No independent user reviews or testimonials available.
- −Only found a single founder post — no real community.
- −Limited to three IaC frameworks — no CDK or Ansible.
- −Effectiveness at scale is completely unproven.
- −False positive rates and configuration noise are unknown.
- • Exact per-seat pricing not publicly listed
- • Self-hosted likely requires infrastructure and maintenance effort
Viability Score
How well maintained and how widely used is Terracotta AI? Built from what the vendor actually publishes (docs, changelog, tutorials, integrations, pricing), whether the site is live, and how much real users discuss it. How we calculate this
Last calculated: October 2026
How we score →Key Features
- Automated PR review for Terraform and OpenTofu
- Security misconfiguration detection (public S3, SSH open to 0.0.0.0/0, overly permissive IAM)
- Custom guardrails written in plain English, no Rego required
- Per-resource cost analysis with monthly and annual projections
- Cost thresholds that flag changes above a set dollar impact
- Field-level drift detection across 119 AWS resource types
- Blast radius analysis showing dependent resources and production impact
- Pre-existing vs. newly introduced finding classification
- Auto-remediation that opens a fix PR on the branch
- Inline PR comments on GitHub and GitLab
- Slack alerts for policy and guardrail violations
- Compliance findings with exportable, tamper-evident audit trail
- Module and pattern checks pointing to the version the team standardized on
- Contextual AI assistant within the review (What's the main risk?, Explain guardrail violations)
- SOC 2 Type II and HIPAA compliance posture stated by the vendor
About Terracotta AI
Terracotta AI is an AI review layer for Terraform and OpenTofu pull requests, built for platform, DevOps, and SRE teams. Connect a GitHub or GitLab repo and every PR gets a review comment covering four things: security misconfigurations (a security group opening SSH to 0.0.0.0/0, an unencrypted S3 bucket), compliance findings, per-resource cost impact with annual projections, and drift — including pre-existing drift Terracotta surfaces inside the diff rather than only flagging newly introduced problems. Reviews also show blast radius, so a change to a shared subnet flags the 12 resources across 3 services that depend on it, plus module and pattern checks that point engineers at the version the rest of the team already moved to. There is nothing to install in your pipeline and no workflow change; findings land where the team already reads code, with an 'Open fix PR' option for remediation and Slack alerts for violations. The vendor states SOC 2 Type II and HIPAA compliance and is backed by Y Combinator. Terracotta is deliberately narrow — infrastructure as code, not application code — so it complements rather than replaces a general code-review tool.
Behind the Verdict
Terracotta AI's pitch is narrow on purpose, and that narrowness is the product. Most IaC tooling asks you to bolt a scanner into CI and then go read a report somewhere else. Terracotta instead attaches to the Git provider you already use — GitHub or GitLab — and returns a single PR comment with counts by severity, the top finding written in plain English, cost impact, and a one-click fix PR. In the sample review the vendor publishes, a t2.micro to t3.xlarge change returns 3 high-severity findings, a failed guardrail, +$243/mo in cost impact, and the note that the SSH ingress rule was pre-existing rather than introduced by this PR — that last distinction is the kind of detail that stops teams from drowning in repeat noise.\n\nStrengths: the four review surfaces (security, guardrails, cost, blast radius) cover questions a PR reviewer actually asks before clicking merge; cost analysis is per-resource with annual projections and a threshold you set, so anything above it gets flagged before it ships; drift detection reports field-level changes and deleted resources that never passed through code; guardrails are written in plain English rather than Rego; the module and pattern checks nudge engineers toward the version the rest of the org already standardized on, which is a quiet onboarding win.\n\nWhere it fits: platform teams enforcing standards across many repos, SREs trying to cut configuration-caused incidents, security engineers who want findings before deployment with something exportable at audit time. The vendor states SOC 2 Type II and HIPAA compliance and shows a governance dashboard framing for compliance owners.\n\nWhere it does not fit: teams whose Git provider is neither GitHub nor GitLab, teams whose IaC is Kubernetes manifests rather than Terraform-family code, and application-code review. If your only need is syntax and formatting on a solo repo, the heavier governance surface is more tool than you need. The honest caveat is depth of language coverage — a Terraform-specialist reviewer will not cover every stack you run, so plan for a companion scanner if you also maintain Pulumi or CloudFormation estates at scale.
Researching Terracotta AI? Get your full AI stack in 60 seconds.
Free, no signup — tell us your goal and get tools matched to your budget & existing stack.
Real-world workflow fit
Concrete scenarios for the personas Terracotta AI actually fits — and what changes day-one when you adopt it.
Opens a PR that resizes an RDS instance from db.t3.medium to db.r6g.2xlarge
Outcome: Terracotta comments on the PR with the +$340/mo impact, notes that staging runs the same instance class and would add $290/mo there, and the engineer resizes staging first — before the cost ships
Reviews a PR from a repo still on vpc module v2.1 while six of seven repos moved to v4.0
Outcome: The module check points the author at v4.0 and the missing private subnet defaults, so the PR gets corrected in review instead of drifting into production
A security group ingress rule and two tag sets were edited in the console over the weekend
Outcome: The drift report shows the field-level modifications and deleted resources that the state file does not mention, and flags that the same runbook caused this drift four times this quarter
Use Cases
- Catch an SSH rule opened to 0.0.0.0/0 before it merges to production
- See a PR's cost impact per resource — e.g. +$243/mo from an instance resize — before you approve it
- Surface console edits and deleted resources that your state file does not know about
- Flag a change to a shared VPC with the 12 dependent resources across 3 services
- Point a new engineer at the vpc module version the rest of the org already uses
- Generate a review comment your security team can point to at audit time
- Block changes that violate a plain-English guardrail the platform team set
Limitations
- Terracotta AI is a Terraform-family reviewer: the vendor's own review surfaces are described for Terraform pull requests, so Pulumi, CloudFormation, and Kubernetes-manifest workflows get less of the product than Terraform does.
- It attaches to GitHub and GitLab; if your code lives elsewhere, there is no path shown.
- Custom guardrails are authored in plain English per the vendor, but the underlying policy files are still configuration you have to maintain and get right.
- Cost analysis is presented per resource with an annual projection, which is an estimate of list-price impact, not a bill — treat large numbers as a prompt to look rather than a forecast.
- Drift detection is documented across 119 AWS resource types, so non-AWS drift coverage should not be assumed.
- Like any AI reviewer, findings need a human decision: Terracotta surfaces the SSH ingress rule and the unencrypted bucket, but someone still has to judge whether the change is intentional.
- Enterprise-only items such as SSO/SAML, self-hosted deployment, custom audit log export, and air-gapped support mean larger organizations run a sales cycle before they run the product.
- Large Terraform state files can slow review times.
as of 2026-09-26
Verification history
We have re-verified Terracotta AI 8 times since . Each pass re-reads the vendor's own pages and re-checks every listed field against that evidence; passes where nothing had changed are marked as such.
- — re-checked, vendor evidence unchanged
- — re-checked, vendor evidence unchanged
- — re-checked, vendor evidence unchanged
- — re-checked, vendor evidence unchanged
- — re-checked, vendor evidence unchanged
- — re-checked, vendor evidence unchanged
Showing the 6 most recent of 8 verification passes.
Free to cite with attribution — this page re-verifies continuously.
12-month cost
Project the real annual outlay, including the implied monthly cost when only an annual tier is published.
Vendor list price only. Add-on usage, seat overages, and contract minimums are surfaced under Hidden costs & gotchas.
Plans compared
For each published Terracotta AI tier: who it actually fits, and what it adds vs. the previous tier. Cross-reference the cost calculator above for projected annual outlay.
Free
$0/mo
Ideal for
An individual developer or one infra repo where you want review comments on Terraform PRs without a procurement conversation.
What this tier adds
Free entry point: reviews for an individual, security and compliance checks, and basic drift detection.
Team
$49/seat/mo
Ideal for
A platform or DevOps team of several engineers merging infrastructure across multiple repos who need enforcement, cost control, and audit output.
What this tier adds
Adds the full command center, plain-English custom guardrails, cost governance with approval thresholds, drift detection across 119 AWS resource types, auto-remediation proposals, the compliance dashboard, and exportable audit-ready reports.
Enterprise
Contact sales
Ideal for
Regulated or security-constrained organizations that need to control identity, hosting, and log export — healthcare and finance are the segments the vendor names.
What this tier adds
Adds SSO/SAML, a self-hosted deployment option, custom audit log export, and air-gapped environment support on top of Team.
Where the pricing makes sense
The company stage and team size where Terracotta AI's pricing actually pencils out — and where peers do it cheaper.
The vendor publishes a free entry point for individuals, a Team tier at $49/seat/mo, and an Enterprise tier at contact sales with SSO/SAML, self-hosted deployment, custom audit log export, and air-gapped support. That puts Terracotta in the same band as other seat-priced developer security tooling: cheaper than an enterprise code-scanning contract, more than a standalone open-source scanner you run yourself. Per-seat pricing means the bill tracks how many engineers merge infrastructure, not how
Setup time & first value
How long it actually takes to get something useful out of Terracotta AI — broken out by persona, not the marketing-page minute.
Connecting a GitHub or GitLab repo is the whole setup — the vendor's framing is 'connect a repo and the next PR gets reviewed,' with nothing installed in your pipeline. Expect the first review comment on your next pull request. Time to a useful signal after that depends on how many repos you connect and how much guardrail policy you write: plain-English guardrails take an afternoon of thinking
Switching to or from Terracotta AI
How to bring data in from common predecessors and how to get it back out — written for the switcher, not the buyer.
- →From manual PR review: connect the repo and let the next PR get an automated security, cost, and drift pass, then keep the human review for intent.
- →From a CI-embedded IaC scanner: leave the pipeline scanner in place for languages Terracotta does not cover and use the PR comment for Terraform-family changes.
- →From Rego-based policy engines: rewrite the rules you care about as plain-English guardrails so engineers can read the policy that blocked them.
- ↗To Checkov or Snyk: keep these if you need broad multi-language IaC scanning and are willing to give up the drift, cost, and blast-radius views Terracotta puts in the PR.
- ↗To your Git provider's native checks: for a single solo repo where you only want syntax and formatting feedback, native CI checks cover that without a review platform.
Integrations
Resources & Guides
Tutorials & Learning
YouTube returned 6 videos for “Terracotta AI”, and we withheld 6: 6 could not be judged, because “Terracotta AI” is a single word that other videos use for other things. We are showing none, because we could not prove any of them are about Terracotta AI.
Official links
Tools that pair well with Terracotta AI
Common stack mates teams adopt alongside Terracotta AI, with the specific reason each pairing earns its keep.
Codacy AI
Codacy AI enforces code review, security scans, and AI governance guardrails inside your IDE and on every pull request.
CodeRabbit
AI code review that reviews, triages, and secures every pull request your team ships.
SonarQube
SonarQube is code verification and governance software that statically analyzes every pull request across 30+ languages and blocks merges that fail your
Featured Head-to-Head Comparisons
Terracotta Ai vs Spider Cloud
Spider Cloud and Terracotta AI serve completely different domains: Spider Cloud is for AI agents needing real-time web data extraction, while Terracotta AI is for DevOps teams enforcing IaC security and compliance. Choose Spider Cloud if you're building LLM-powered tools that require up-to-date, structured web content at scale. Choose Terracotta AI if you manage infrastructure code and need automated, policy-driven PR reviews to catch misconfigurations before deploy.
Terracotta Ai vs Temporal Ai
Temporal AI and Terracotta AI serve completely different purposes: Temporal is for building reliable, stateful workflows (AI agents, microservices) with durable execution, while Terracotta is a narrow IaC security scanner for Terraform/Pulumi PRs. Choose Temporal if you need fault-tolerant orchestration; choose Terracotta if you’re a DevOps team wanting automated infrastructure compliance.
Terracotta Ai vs Voyage Ai
Choose Voyage AI if your priority is high-accuracy retrieval for RAG on domain-specific enterprise data (finance, legal, code) and you need long-context, low-dimensional embeddings. Choose Terracotta AI if you're a DevOps or platform engineer who wants to catch IaC misconfigurations before they reach production. They solve completely different problems—pick the one that matches your workflow.
Cognition Ai vs Terracotta Ai
If you're an enterprise engineering team needing an autonomous agent that plans, codes, and ships production code—especially for complex multi-step tasks or legacy modernization—choose Cognition AI (Devin). If you're a DevOps or security engineer automating IaC reviews for security, compliance, cost, and drift, choose Terracotta AI. They serve different purposes: Devin replaces junior developers; Terracotta protects infrastructure pipelines.
Pieces For Developers vs Terracotta Ai
If you need to remember every piece of context across your dev workflow—code, chats, meetings—Pieces for Developers is the auto-memory you didn't know you needed. If you're responsible for shipping Terraform safely and staying compliant, Terracotta AI's automated PR checks and drift detection are indispensable. They solve entirely different problems; choose based on whether your pain is 'I can't find that snippet' or 'I can't let that misconfig hit production.'
Alternatives to Terracotta AI
View all
Codacy AI
Codacy AI enforces code review, security scans, and AI governance guardrails inside your IDE and on every pull request.
CodeRabbit
AI code review that reviews, triages, and secures every pull request your team ships.
Frequently Asked Questions
Best-of guides
Used Terracotta AI? Help shape our editorial sentiment research.